A locked system used to be the main fear in a ransomware incident. That is no longer the full story. Ransomware Data Theft has turned many attacks into a double crisis, where organizations face both operational disruption and the risk of sensitive information being exposed, sold, or used for further extortion. For business leaders, the financial damage now reaches far beyond recovery costs.
Ransomware is no longer just about encryption
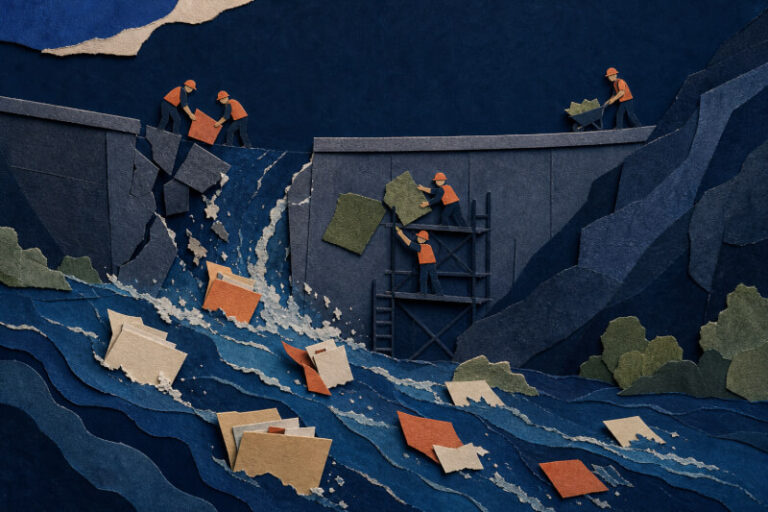
Attack groups increasingly steal data before they encrypt anything. This gives them more pressure points. Even if backups are available and systems can be restored, the threat of leaked contracts, employee records, customer information, or internal communications can keep the incident alive for weeks or months. As a result, ransomware has become a data breach, legal issue, and reputational challenge at the same time.
This shift matters because many organizations still plan for downtime more than disclosure. Backup strategies are important, but they do not prevent stolen data from becoming public. In many cases, executives discover too late that business continuity planning covered system recovery, while incident response planning did not fully address extortion, regulatory reporting, stakeholder communication, or third-party exposure.
The business impact goes well beyond IT
When attackers steal information, the consequences spread quickly across the organization. Security teams may contain the technical incident, but legal teams, compliance leaders, operations managers, and executive leadership often carry the longer-term burden. Customer trust can weaken. Contractual obligations may be triggered. Regulatory scrutiny can increase, especially when personal or sensitive data is involved.
The cost is also harder to predict. Downtime can often be measured in hours or days, but data theft creates a second layer of uncertainty. Organizations may need forensic investigation, breach notification, external counsel, public relations support, and ongoing monitoring for affected parties. In sectors such as healthcare, finance, and manufacturing, the pressure can be even greater because stolen data may affect patient privacy, financial records, or proprietary operational information.
Where many organizations remain exposed
Ransomware campaigns rarely succeed because of one single failure. More often, attackers take advantage of gaps that build up over time. Unmanaged identities, weak remote access controls, limited network visibility, and inconsistent data governance can all make it easier to steal valuable information before anyone notices. Once inside, attackers tend to move toward the systems and repositories that matter most to the business.
Another common issue is assuming that prevention alone is enough. Strong endpoint protection and email security reduce risk, but they do not remove it. Organizations also need to know what data matters most, where it lives, who can access it, and how unusual movement can be detected early. Without that visibility, response teams may restore operations without fully understanding what was taken.
What a stronger response strategy should include
A more effective approach starts with treating ransomware as both an availability threat and a data exposure threat. That means response planning should connect security, legal, operations, and leadership before an incident occurs. The goal is not only to recover systems, but also to reduce the chance that stolen data becomes a lasting business crisis.
- Prioritize sensitive data and map where it is stored
- Limit unnecessary access through stronger identity and privilege controls
- Monitor for unusual data movement, not only malware activity
- Test incident response plans for extortion and disclosure scenarios
- Review backup, segmentation, and recovery processes together
These steps help organizations make better decisions under pressure. They also improve resilience by reducing the value attackers can extract after gaining access. In many cases, the difference between a contained incident and a prolonged crisis comes down to preparation, visibility, and cross-functional coordination.
Choosing the right security support
Ransomware defense is rarely solved by one tool. Most organizations need a combination of identity protection, endpoint security, network controls, backup strategy, monitoring, and incident readiness. The challenge is choosing technologies that fit operational needs without creating more complexity or leaving critical gaps between teams and systems.
Organizations evaluating solutions for ransomware resilience can work with Terrabyte to identify security technologies that align with their risk profile, data exposure concerns, and response requirements. As a cybersecurity distributor and trusted technology partner, Terrabyte helps enterprises assess the right mix of solutions for prevention, detection, containment, and recovery.